Information Security & ISO 27001

Retail stockroom CCTV monitors beside a QR code on a clipboard, illustrating a shadow IT workaround that bypassed data protection sign-off

What the Met Police’s Auror Reprimand Really Teaches About Shadow IT

A LinkedIn Celebration, Six Months Before an Enforcement Notice In April, Auror’s co-founder and the Metropolitan Police’s official account posted on LinkedIn about a retail crime pilot going well. Officers in Lewisham and central London could review CCTV and incident reports submitted by retailers through a platform called Auror, and the positive outcome rate —

What the Met Police’s Auror Reprimand Really Teaches About Shadow IT Read More »
A supermarket worker uses a probe thermometer and clipboard to check the temperature of empty, fogged-up freezer cabinets, with the aisle closed off, after a cyber attack on the store’s refrigeration systems

Defrosted overnight: the French supermarket cyber attack and How it describes my job

When someone asks me what I do for a living, I usually take a breath before answering. Business continuity, crisis management, information security, data protection, emergency planning, exercising, training…. People’s eyes start to glaze over somewhere around the third item, and I can see them filing me under “something in IT” or “health and safety,

Defrosted overnight: the French supermarket cyber attack and How it describes my job Read More »

Risk professional reviewing an AI risk register heat map next to an AI assistant chat window

A Researcher Just Put a Number on Human Extinction. Your Risk Register Needs a Different One.

This week produced three AI stories that look separate but aren’t. Anthropic’s own alignment lead put a number on AI wiping out humanity: a chance he personally puts at more than 10% within the next decade. The company’s latest Threat Intelligence Report disclosed that it has spent the months since December 2025 detecting and blocking

A Researcher Just Put a Number on Human Extinction. Your Risk Register Needs a Different One. Read More »

Close-up of hands adjusting a small brass gear within a larger, intricate clockwork mechanism

A Forgotten Certificate Just Broke Email for Millions. That’s the Real Story.

On Monday evening, Outlook and Exchange Online stopped working. Not for one company, for a meaningful slice of the world. People couldn’t log in. Messages sat unsent. Search returned nothing. IT teams spent hours fielding calls from colleagues who couldn’t do their jobs, because the one tool most of us touch fifty times a day

A Forgotten Certificate Just Broke Email for Millions. That’s the Real Story. Read More »

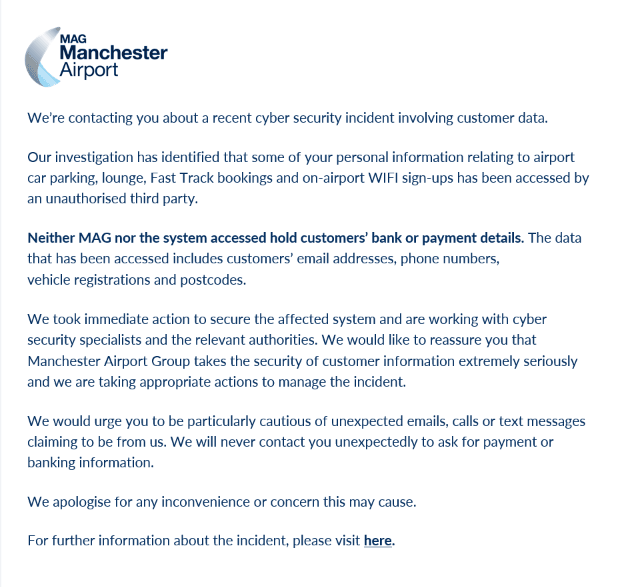
Screenshot of Manchester Airport Group's customer email notifying passengers that car parking, lounge, Fast Track and WiFi data was accessed in a cyber security incident.

I can change a password. I can’t change my number plate.

I got an email last week that a lot of people reading this will also have had. Manchester Airports Group wrote to tell me my data had been caught up in a cyber security incident. In my case it was the car parking, and not the cheap kind either, since I’d paid for it three

I can change a password. I can’t change my number plate. Read More »

An upward trending graph line behind the figure $4.99 million, representing the rising average cost of a data breach.

The Real Cost of a Breach Just Went Up Again — Here’s What the Number Doesn’t Tell You

IBM published its Cost of a Data Breach Report last month, and the headline figure is the one everyone will quote: the global average cost of a breach has hit a record $4.99 million, a 12% increase on last year. In the UK specifically, that average sits at around $4.27 million (£3.13 million). Numbers like

The Real Cost of a Breach Just Went Up Again — Here’s What the Number Doesn’t Tell You Read More »

A small business leadership team of four reviews a recovery plan together around a meeting table, discussing priorities calmly and analytically

What the NCSC’s new incident recovery guidance gets right, and where it falls short

On 29 July, the NCSC published What To Do When Cyber-Attacks Disrupt Your Organisation, a detailed framework covering the first hours of a disruptive attack through to the months of rebuild that follow. It’s well timed. Attack volumes are up, and the guidance is clear-eyed about something many boards still underestimate: recovery from a serious

What the NCSC’s new incident recovery guidance gets right, and where it falls short Read More »

Smartphone capturing an augmented reality scan of a city street, illustrating spatial data collection for AI training

When Catching Pokémon Becomes Training Data for War: What the Niantic-Vantor Story Teaches Us About Data Protection

Few stories illustrate the gap between “what data subjects think they agreed to” and “what actually happens to their data” as vividly as the one that broke in June 2026. Millions of people who spent years scanning parks, murals and landmarks to catch Pokémon on their smartphones have discovered that those scans didn’t stay in

When Catching Pokémon Becomes Training Data for War: What the Niantic-Vantor Story Teaches Us About Data Protection Read More »

Close-up of a woman's wrist wearing a fitness tracker at a kitchen table, illustrating everyday wearable data collection

Who knew you were pregnant before you did?

Who knew you were pregnant before you did? There’s a story doing the rounds this week about a woman whose fitness tracker flagged her pregnancy weeks before a test did. Elevated resting heart rate, a shift in temperature, the usual pattern. It’s a nice human interest story, and it’s also, if you sit with it

Who knew you were pregnant before you did? Read More »

what makes a supplier risk assessment

What Makes a Supplier (And When a Tool Is Not Simply a Tool)

What Makes a Supplier (And When a Tool Is Not Simply a Tool) Every organisation I’ve worked with over the years has a supplier list. It sits somewhere in a spreadsheet, gets reviewed once a year around audit time, and contains the names you’d expect: the IT support company, the payroll provider, maybe a facilities

What Makes a Supplier (And When a Tool Is Not Simply a Tool) Read More »