data breach

An empty drawer pulled open from a long row of grey metal filing cabinets in a dimly lit storage room

The Social Media Ban Will Check Adults Too. So Who Ends Up Holding Your Passport?

This morning Ofcom published its assessment of how social media firms could check that their users are 16 or over when the under-16s ban comes into force next year. It names four methods it considers capable of being “highly effective”: photo ID matching, banking checks, digital ID services and facial age estimation. Most of the

The Social Media Ban Will Check Adults Too. So Who Ends Up Holding Your Passport? Read More »
Retail stockroom CCTV monitors beside a QR code on a clipboard, illustrating a shadow IT workaround that bypassed data protection sign-off

What the Met Police’s Auror Reprimand Really Teaches About Shadow IT

A LinkedIn Celebration, Six Months Before an Enforcement Notice In April, Auror’s co-founder and the Metropolitan Police’s official account posted on LinkedIn about a retail crime pilot going well. Officers in Lewisham and central London could review CCTV and incident reports submitted by retailers through a platform called Auror, and the positive outcome rate —

What the Met Police’s Auror Reprimand Really Teaches About Shadow IT Read More »

Empty chair and staff lanyard beside a hospital computer showing a patient record with an access alert, after NHS snooping suspension

NHS Snooping Crackdown: Suspension Is the Easy Part

Back in June I wrote about three hospital trusts where dozens of staff had looked at the records of patients who happened to be in the news: the Southport victims treated at Aintree, the Nottingham stabbing victims, and the three-year-old injured at a zoo near Huntingdon who was taken to Addenbrooke’s. What struck me most

NHS Snooping Crackdown: Suspension Is the Easy Part Read More »

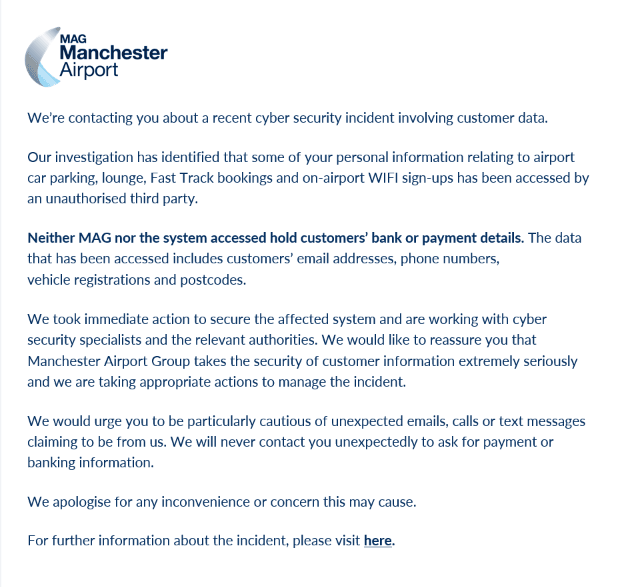
Screenshot of Manchester Airport Group's customer email notifying passengers that car parking, lounge, Fast Track and WiFi data was accessed in a cyber security incident.

I can change a password. I can’t change my number plate.

I got an email last week that a lot of people reading this will also have had. Manchester Airports Group wrote to tell me my data had been caught up in a cyber security incident. In my case it was the car parking, and not the cheap kind either, since I’d paid for it three

I can change a password. I can’t change my number plate. Read More »

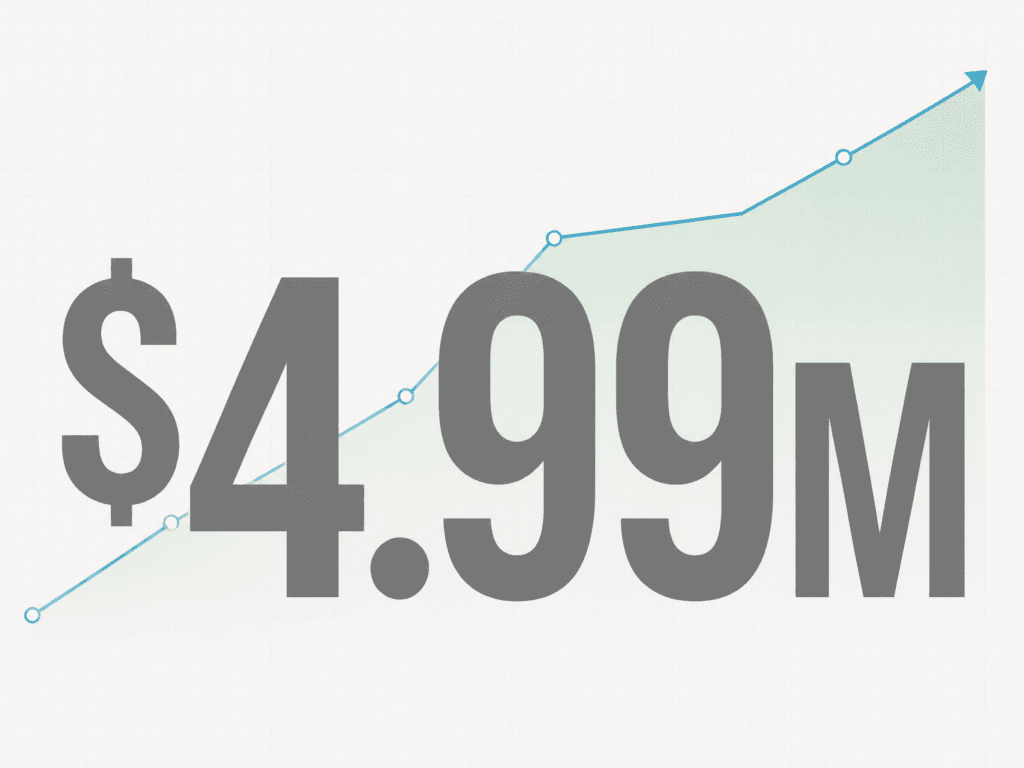
An upward trending graph line behind the figure $4.99 million, representing the rising average cost of a data breach.

The Real Cost of a Breach Just Went Up Again — Here’s What the Number Doesn’t Tell You

IBM published its Cost of a Data Breach Report last month, and the headline figure is the one everyone will quote: the global average cost of a breach has hit a record $4.99 million, a 12% increase on last year. In the UK specifically, that average sits at around $4.27 million (£3.13 million). Numbers like

The Real Cost of a Breach Just Went Up Again — Here’s What the Number Doesn’t Tell You Read More »

Close-up of a woman's wrist wearing a fitness tracker at a kitchen table, illustrating everyday wearable data collection

Who knew you were pregnant before you did?

Who knew you were pregnant before you did? There’s a story doing the rounds this week about a woman whose fitness tracker flagged her pregnancy weeks before a test did. Elevated resting heart rate, a shift in temperature, the usual pattern. It’s a nice human interest story, and it’s also, if you sit with it

Who knew you were pregnant before you did? Read More »

A gloved hand on a computer mouse next to a keyboard, with a patient record displayed on a hospital computer screen in the background

The NHS doesn’t have a data security problem. It has a culture problem.

The NHS doesn’t have a data security problem. It has a culture problem. This week, Cambridge University Hospitals referred itself to the Information Commissioner’s Office after it emerged that around 40 members of staff had accessed the medical records of a three-year-old boy injured in a crocodile attack. The child was treated at Addenbrooke’s following

The NHS doesn’t have a data security problem. It has a culture problem. Read More »

A blurred figure walks past rows of colour-coded medical records files in a hospital records room

48 staff. No dismissals. No ICO investigation. The Southport records breach tells us everything we need to know about insider threat.

48 staff. No dismissals. No ICO investigation. The Southport records breach tells us everything we need to know about insider threat. When the news broke this week that 48 NHS staff had inappropriately accessed the medical records of Southport attack victims — and that the highest sanction any of them received was a final written

48 staff. No dismissals. No ICO investigation. The Southport records breach tells us everything we need to know about insider threat. Read More »

Illustration of data breach with lock icon and spreadsheet background.

The Afghan Data Breach – A Wake-Up Call for Public Sector Data Governance

️ The Afghan Data Breach – A Wake-Up Call for Public Sector Data Governance In July 2025, the veil of secrecy was finally lifted on one of the most catastrophic data breaches in UK government history. A spreadsheet leaked by a Ministry of Defence (MoD) official exposed the personal details of nearly 19,000 Afghan nationals […]

The Afghan Data Breach – A Wake-Up Call for Public Sector Data Governance Read More »